Security
How Tessavra separates and protects conversation data, and what is still being built.
Customer data is separated per organisation by row-level security, tested on a local stack. Roles decide who can open what. Tessavra has no independent penetration test, no certification and no published subprocessor list.
Access
Roles decide who can open what.
Roles decide who can open a transcript, a finding or an administration screen, and a feature is off for an organisation until it is granted. Customer data is separated per organisation by row-level security. That has been tested on a local stack, not in a hosted environment, and there has been no independent penetration test. Membership and privileged-access changes are recorded in append-only logs. A Microsoft Entra single sign-on framework is in development, and no identity provider has been connected in a hosted environment.
- Role-based access, in development
- Row-level security per organisation, tested locally
- Entra single sign-on framework, in development
Governance
A finding carries its citation and its review state.
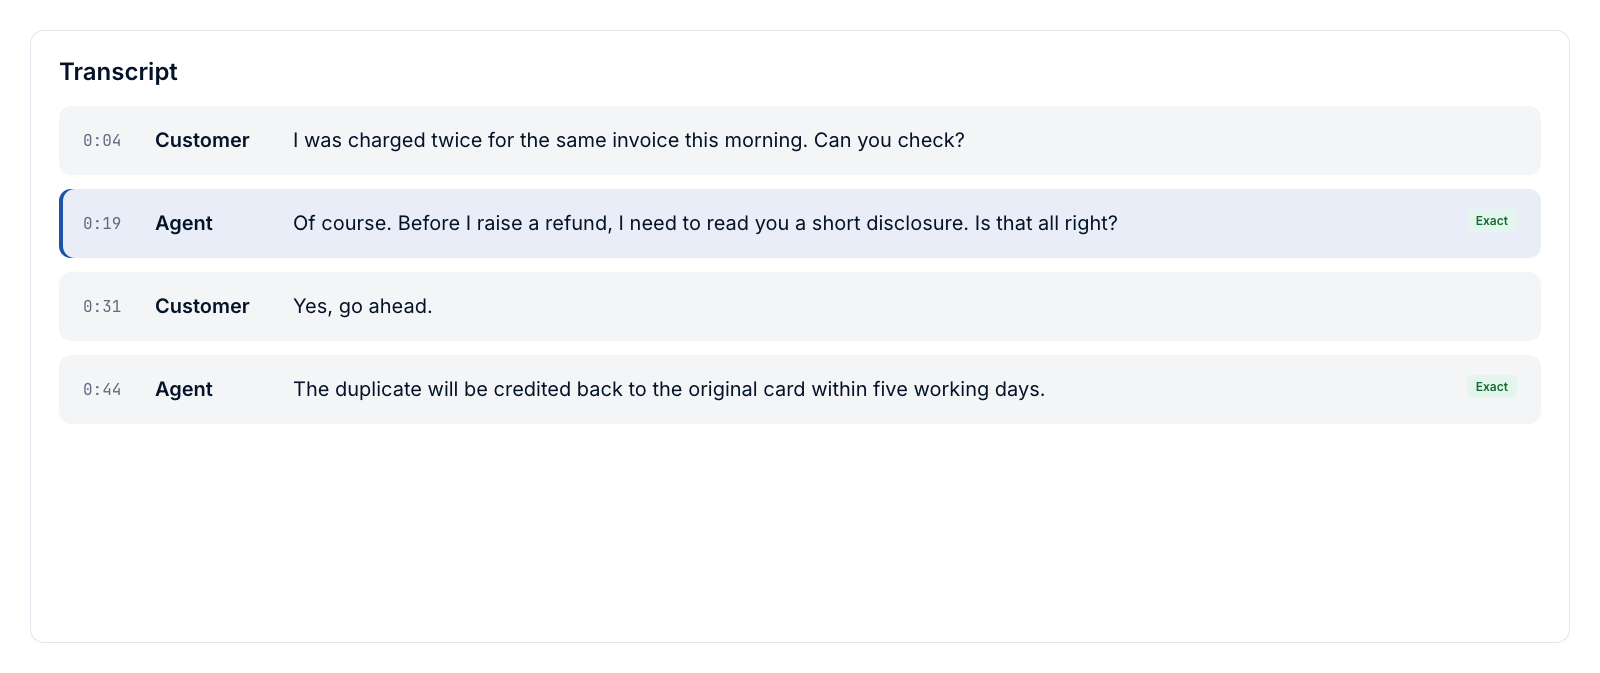
A finding can be marked not reviewed, in progress or reviewed, and a person sets that state. Where a finding cites audio, the citation carries a confidence marker such as Exact or Unverified. Unverified means a person should listen before they treat it as the record. Citation accuracy has not yet been evaluated.
- A review state a person sets
- The line the finding cites
- A confidence marker on audio citations
Retention and legal hold are in development.
A retention policy engine
Per-class timers are built and tested locally. No default retention period is claimed.
Legal hold
Meant to pause deletion for named conversations while a matter is open. Not yet verified against every deletion path.
What exists today
Audio expiry runs locally. Transcripts and insights are not erased by it, and self-service export and erasure are not available.
Screen sharing, on the desktop.
Excluded from screen sharing
On macOS the Bar and the Panel are excluded from screen sharing, and an organisation can lock the setting. The Workspace window stays shareable, and other capture tools may still show the Bar and the Panel.
A disclosure marker
The person on the call marks that the customer was told the call is recorded. Tessavra does not announce the recording to the other party.
Private notes
Private notes are excluded from shares, copies and emails. The person who wrote a note can still export their own.
What this page does not claim
No SOC 2, ISO 27001, HIPAA, PCI or GDPR certification. No independent penetration test, uptime commitment or data-residency commitment. No multi-factor authentication, no SCIM directory sync and no SAML sign-in. No self-service data export or erasure, no default retention period and no public API. Payment-capture blocking is not claimed. No subprocessor list is published. If you need security documentation for a review, write to hello@tessavra.com.
Read more.
Talk through the controls you need.
Request a demo and bring the questions from your security review.
Request a demo